What Is HTTP vs HTTPS? Why It Matters
HTTP vs HTTPS explained in plain terms: how each protocol works, why encryption matters, and how HTTPS affects SEO, user trust, and site security.
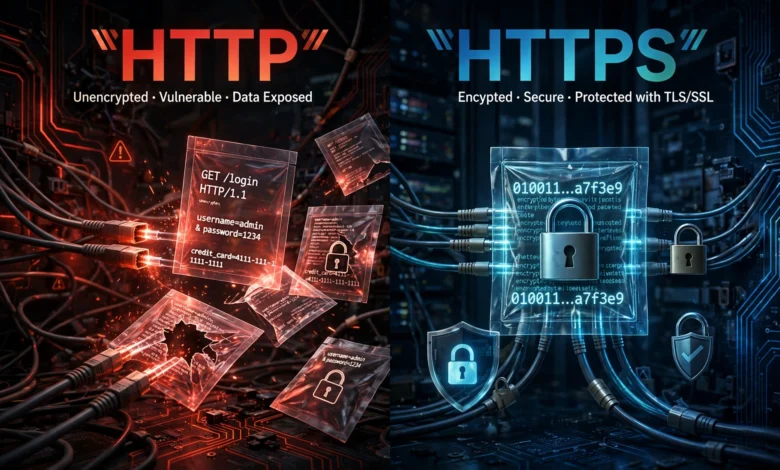
HTTP vs HTTPS looks like a tiny difference. One extra letter in the address bar, and most people never think about it. But that single “S” decides whether the information you send to a website travels in a sealed envelope or on the back of a postcard that anyone along the way can read.Every time you log in to an account, fill out a contact form, or buy something online, your browser is exchanging data with a server. With plain HTTP, that data moves as readable text. With HTTPS, it gets encrypted before it leaves your device, so even if someone intercepts it, they see nothing useful.
This matters for everyone. Visitors want to know their passwords and card numbers are safe. Site owners want people to trust them enough to stay, sign up, and pay. And search engines like Google now openly favor secure websites, while browsers flag unencrypted pages with a “Not Secure” label that scares off visitors fast.
In this guide, we’ll break down the difference between HTTP and HTTPS in plain language. You’ll see how each protocol works, what an SSL certificate actually does, why HTTPS has become the default for the modern web, and how it affects your rankings. If you run a website that still uses HTTP, you’ll also get a clear, step-by-step path for making the switch without losing traffic.
What Is HTTP? The Foundation of the Web
HTTP stands for Hypertext Transfer Protocol. It’s the set of rules browsers and servers use to talk to each other. When you type a web address and hit enter, your browser sends an HTTP request to the server, and the server sends back an HTTP response containing the page, images, scripts, and everything else you see.
HTTP was created in the early 1990s, when the web was mostly a place for researchers to share documents. Security wasn’t part of the design because nobody expected people to be shopping, banking, and filing taxes through a browser. So HTTP sends everything in plain text.
How HTTP Works Step by Step
Here’s what happens during a basic HTTP exchange:
- You enter a URL or click a link.
- Your browser looks up the server’s IP address through DNS.
- The browser opens a connection to the server, usually on port 80.
- It sends a request, such as “GET /about-us”.
- The server responds with a status code (like 200 OK) and the page content.
- Your browser renders what it received.
Simple and fast. The trouble is that every step after the connection opens is readable by anyone sitting between you and the server.
The Core Weakness of HTTP
Because HTTP doesn’t encrypt anything, the data can be seen or changed in transit. That includes:
- Login usernames and passwords
- Credit card details entered on checkout pages
- Personal information in contact or signup forms
- Cookies that keep you logged in
- The pages themselves, which can be altered before they reach you
On a public Wi-Fi network at a café or airport, this is a real risk, not a theoretical one.
What Is HTTPS? HTTP With a Security Layer
HTTPS stands for Hypertext Transfer Protocol Secure. It’s the same HTTP protocol running inside an encrypted connection created by TLS (Transport Layer Security). You’ll often hear people call this SSL, which is TLS’s older predecessor. SSL itself is now retired because of known flaws, but the name stuck, which is why we still say “SSL certificate.”
With HTTPS, the conversation between your browser and the server is scrambled so only the two of them can read it. It typically runs on port 443 instead of port 80.
What HTTPS Protects
HTTPS gives you three important guarantees:
- Encryption: Data is scrambled in transit, so eavesdroppers see gibberish.
- Integrity: Data can’t be quietly modified along the way. If someone tampers with it, the connection breaks.
- Authentication: The certificate proves you’re talking to the real website, not an impostor pretending to be it.
That third point often gets overlooked. Encryption alone isn’t enough if you’re securely connected to the wrong server. The certificate is what confirms the identity on the other end.
If you want a deeper technical look, Cloudflare has a clear explainer on how HTTPS and TLS encryption work.
HTTP vs HTTPS: The Key Differences at a Glance
Now that you know what each one is, here’s a direct comparison of HTTP vs HTTPS across the points that matter most.
| Feature | HTTP | HTTPS |
|---|---|---|
| Full name | Hypertext Transfer Protocol | Hypertext Transfer Protocol Secure |
| Default port | 80 | 443 |
| Encryption | None, plain text | Encrypted with TLS |
| Certificate needed | No | Yes, an SSL/TLS certificate |
| Data integrity | Can be altered in transit | Tampering is detected |
| Server authentication | No | Yes |
| Browser label | “Not Secure” warning | Padlock or neutral secure icon |
| SEO impact | No ranking benefit | Confirmed lightweight ranking signal |
| Modern features | Many blocked | Supports HTTP/2, HTTP/3, and newer browser APIs |
The short version: HTTP is an open conversation, and HTTPS is a private one with ID checked at the door.
How HTTPS Encryption Works (Without the Jargon)
You don’t need to be a cryptographer to understand the basics of TLS encryption. It all starts with something called the SSL/TLS handshake, which happens in a fraction of a second before any page loads.
The SSL/TLS Handshake in Plain Terms
Think of it like two people agreeing on a secret code before talking in a crowded room:
- Hello: Your browser tells the server which encryption methods it supports.
- Certificate check: The server sends its SSL certificate. Your browser checks that it was issued by a trusted authority, hasn’t expired, and matches the domain you’re visiting.
- Key exchange: Using public key cryptography, the two sides agree on a shared secret key without ever sending that key openly.
- Secure session: From here on, all data is encrypted with that session key, which is fast and efficient.
With TLS 1.3, the current standard, this handshake is quicker than older versions, so the performance cost of HTTPS is tiny.
Public and Private Keys
Every SSL certificate is tied to a key pair:
- The public key is shared openly and used to start the secure exchange.
- The private key stays on the server and is never shared.
Data locked with the public key can only be unlocked with the matching private key. That’s why keeping the private key safe is critical for any site owner.
Types of SSL Certificates
Not all certificates are the same. The main types are:
- Domain Validated (DV): Confirms you control the domain. Quick, cheap or free, and perfectly fine for most blogs and small business sites.
- Organization Validated (OV): Also verifies the business behind the site. Common for companies that want an extra layer of identity checking.
- Extended Validation (EV): The strictest vetting. It used to show a green company name in the address bar, but browsers dropped that display years ago, so its visible advantage is mostly gone.
- Wildcard certificates: Cover a domain and all its subdomains, like shop.example.com and blog.example.com.
- Multi-domain (SAN) certificates: Cover several different domains with one certificate.
For most websites, a free DV certificate from Let’s Encrypt, the nonprofit certificate authority, does the job just as well as a paid one when it comes to encryption strength.
7 Powerful Reasons HTTPS Matters for Every Website
This is where HTTP vs HTTPS stops being a technical detail and becomes a business decision. Here are seven reasons HTTPS is no longer optional.
1. It Protects Your Visitors’ Data
The most obvious reason is data encryption. Any site with a login, a form, a search bar, or a checkout is collecting information from people. HTTPS keeps that information private while it travels. Even a simple newsletter signup collects an email address, and people have a right to expect that it won’t be exposed.
2. It Blocks Man-in-the-Middle Attacks
A man-in-the-middle attack happens when someone secretly positions themselves between a user and a website. On HTTP, they can read traffic, steal session cookies, inject ads or malware into pages, or redirect users to fake login screens. HTTPS makes this dramatically harder because the attacker can’t read or alter encrypted traffic, and they can’t fake a valid certificate for your domain.
3. Browsers Warn Users About HTTP Sites
Since 2018, Google Chrome has labeled all HTTP pages as “Not Secure.” Firefox, Safari, and Edge show similar warnings, especially on pages with password or payment fields. The “Not Secure” warning is one of the fastest ways to lose a visitor. Most people won’t read the details. They’ll just see the word “Not Secure” and leave.
Browsers are also moving toward loading HTTPS by default and showing stronger warnings before opening HTTP pages at all. Google has announced plans to make its “Always Use Secure Connections” setting the default in Chrome, which means HTTP sites will face even more friction going forward.
4. HTTPS Is a Google Ranking Signal
Google confirmed back in 2014 that HTTPS is a ranking factor. You can read the original announcement on the Google Search Central blog about HTTPS as a ranking signal. It’s described as a lightweight signal, so switching to HTTPS won’t rocket a weak page to the top. But when two pages are otherwise similar in quality, the secure one has an edge. HTTPS is also part of Google’s broader page experience considerations.
5. It Builds Trust and Improves Conversions
People have learned to look for the padlock, even if they don’t fully understand what it means. A secure website feels more professional and trustworthy. That trust shows up in behavior: lower bounce rates, more form submissions, and more completed purchases. If you sell anything online, HTTPS is basic credibility.
6. It Unlocks Faster, Modern Web Features
Here’s something many people don’t realize: HTTPS can actually make your site faster. Major browsers only support HTTP/2 and HTTP/3 over encrypted connections. These newer protocols load multiple files at once and cut down on delays, which often more than makes up for the small cost of encryption.
Many modern browser features also require HTTPS, including:
- Geolocation
- Service workers and progressive web apps (PWAs)
- Push notifications
- Camera and microphone access
- Payment Request API
If your site runs on HTTP, you’re locked out of all of these.
7. It Helps With Compliance and Privacy Rules
Privacy laws like GDPR and industry standards like PCI DSS (for handling card payments) expect personal data to be protected in transit. HTTPS is one of the most basic ways to meet that expectation. Running a site that collects personal data over plain HTTP can create legal and financial risk, not just a technical one.
HTTP vs HTTPS for SEO: What Actually Changes
Let’s be realistic about the SEO side of HTTP vs HTTPS, because there’s a lot of exaggeration out there.
What HTTPS Does for Rankings
- It’s a confirmed HTTPS ranking signal, though a small one.
- It prevents referral data loss. When traffic moves from an HTTPS site to an HTTP site, the referrer information is usually stripped, so your analytics show it as “direct” traffic. On HTTPS, you keep more accurate referral data.
- It supports better user signals. Visitors who aren’t scared off by warnings tend to stay longer and engage more.
- Google prefers to index the HTTPS version of a page when both versions exist.
What HTTPS Doesn’t Do
- It won’t fix thin or unhelpful content.
- It won’t replace good backlinks, strong internal linking, or solid on-page SEO.
- It won’t help if the migration is done badly and causes broken links or duplicate content.
Think of HTTPS as a baseline requirement, like having a mobile-friendly design. It’s expected. Not having it hurts you more than having it helps you.
Common HTTPS Problems and How to Avoid Them
Switching to HTTPS is usually smooth, but a few issues come up again and again.
Mixed Content Warnings
Mixed content happens when a page loads over HTTPS but some resources, like images, scripts, or stylesheets, still load over HTTP. Browsers may block those files or remove the padlock. The fix is to update all internal links and resource URLs to HTTPS, or use relative URLs.
Expired Certificates
An expired certificate triggers a full-page browser warning that stops most visitors cold. Certificates also have shorter lifespans than they used to, and the industry is moving toward even shorter validity periods over the next few years. Set up automatic renewal (Let’s Encrypt and most hosts support this) so you never have to remember manually.
Redirect Chains and Loops
If HTTP redirects to HTTPS, which then redirects to www, which then redirects again, you’ve built a chain that slows pages down and wastes crawl budget. Aim for a single 301 redirect from any old URL straight to its final HTTPS version.
Certificate Name Mismatch
If your certificate covers example.com but not www.example.com, visitors on the www version will see an error. Make sure your certificate covers every hostname you use.
How to Move From HTTP to HTTPS Without Losing Traffic
If your site still uses HTTP, here’s a practical checklist for a clean migration.
- Get an SSL certificate. Check your hosting dashboard first. Many hosts offer free certificates with one click.
- Install and test it. Load your site with https:// and confirm the padlock appears with no errors.
- Update internal links. Change links, images, scripts, and stylesheets to HTTPS. On WordPress, a search-and-replace tool in the database handles this quickly.
- Set up 301 redirects. Permanently redirect every HTTP URL to its HTTPS equivalent at the server level.
- Update canonical tags. Make sure every canonical tag points to the HTTPS version.
- Update your XML sitemap and robots.txt. Both should reference HTTPS URLs.
- Add the HTTPS property in Google Search Console and Bing Webmaster Tools. Submit the new sitemap so search engines pick up the change quickly.
- Enable HSTS. HTTP Strict Transport Security tells browsers to always use HTTPS for your domain, closing the small gap before a redirect happens. Start with a short max-age and increase it once you’re confident everything works.
- Update external references where you can. Change your URL on social profiles, business listings, and paid ad campaigns.
- Monitor for a few weeks. Watch rankings, crawl errors, and traffic. A brief wobble is normal. A sustained drop usually points to a redirect or canonical problem.
Done carefully, most sites see no lasting traffic loss, and many see small gains over time.
HTTP vs HTTPS: Common Myths, Cleared Up
A few misconceptions still keep people on HTTP longer than they should be.
“My site doesn’t collect data, so I don’t need HTTPS.”
Even a simple blog benefits. Without HTTPS, anyone on the network can alter your pages before they reach readers, inject ads, or track what visitors read. Plus, browsers will still label your site “Not Secure.”
“HTTPS makes websites slow.”
This was partly true fifteen years ago. Today, with TLS 1.3 and HTTP/2 or HTTP/3, HTTPS sites are often faster than their HTTP versions.
“SSL certificates are expensive.”
Free certificates from Let’s Encrypt offer the same encryption strength as paid ones. Paid certificates mainly add organization validation, warranties, or support.
“The padlock means a site is safe.”
Not quite. The padlock only means the connection is encrypted and the domain matches the certificate. Scammers can get certificates too. HTTPS protects data in transit, but it doesn’t tell you whether the site’s owner is honest.
Conclusion
The difference between HTTP and HTTPS comes down to privacy, trust, and credibility: HTTP sends data as readable text that anyone on the network can see or change, while HTTPS wraps that same conversation in TLS encryption, verifies the site’s identity with an SSL certificate, and makes sure nothing gets altered along the way.
For visitors, that means safer logins, forms, and payments; for site owners, it means avoiding the “Not Secure” warning, gaining a small but real HTTPS ranking signal, unlocking faster protocols like HTTP/2 and HTTP/3, and meeting basic privacy expectations. Certificates are free, setup is often a single click, and a careful migration with proper 301 redirects protects your traffic, so when it comes to HTTP vs HTTPS, there’s simply no good reason to stay on the unsecured side of the web.